Two-part investigation attributing the theft of $46M in U.S. Government-held crypto to John Daghita, known online as “Lick.” An arrest and a large recovery of funds followed.
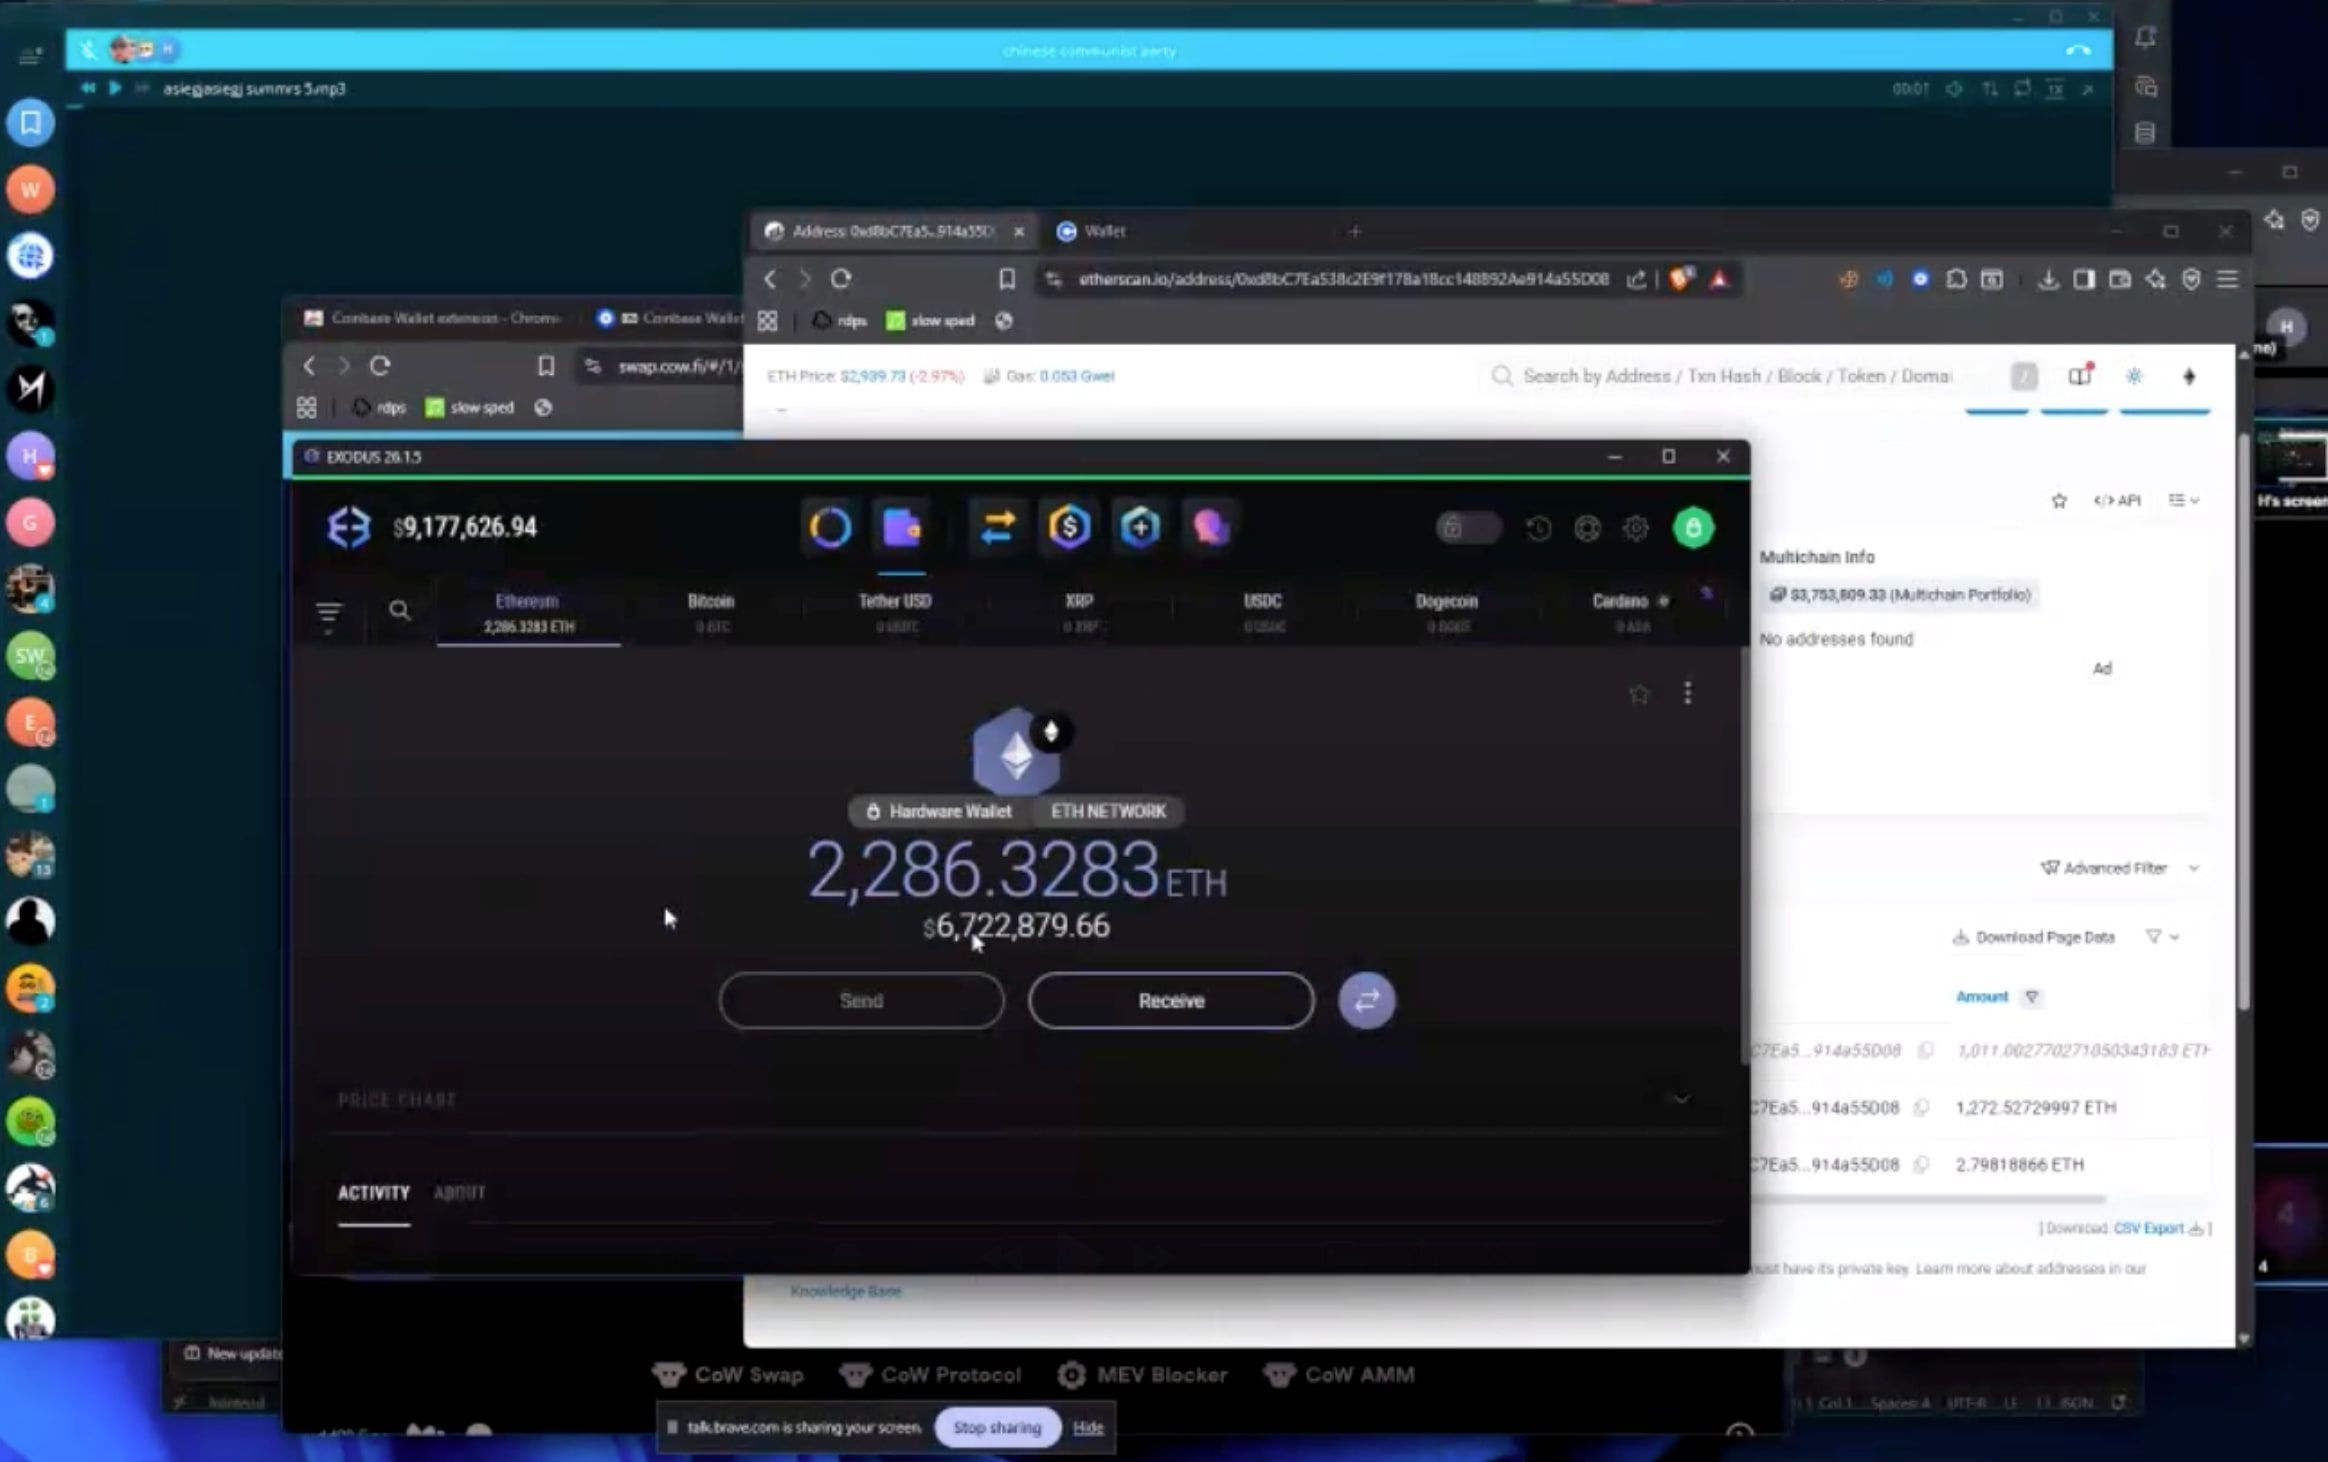
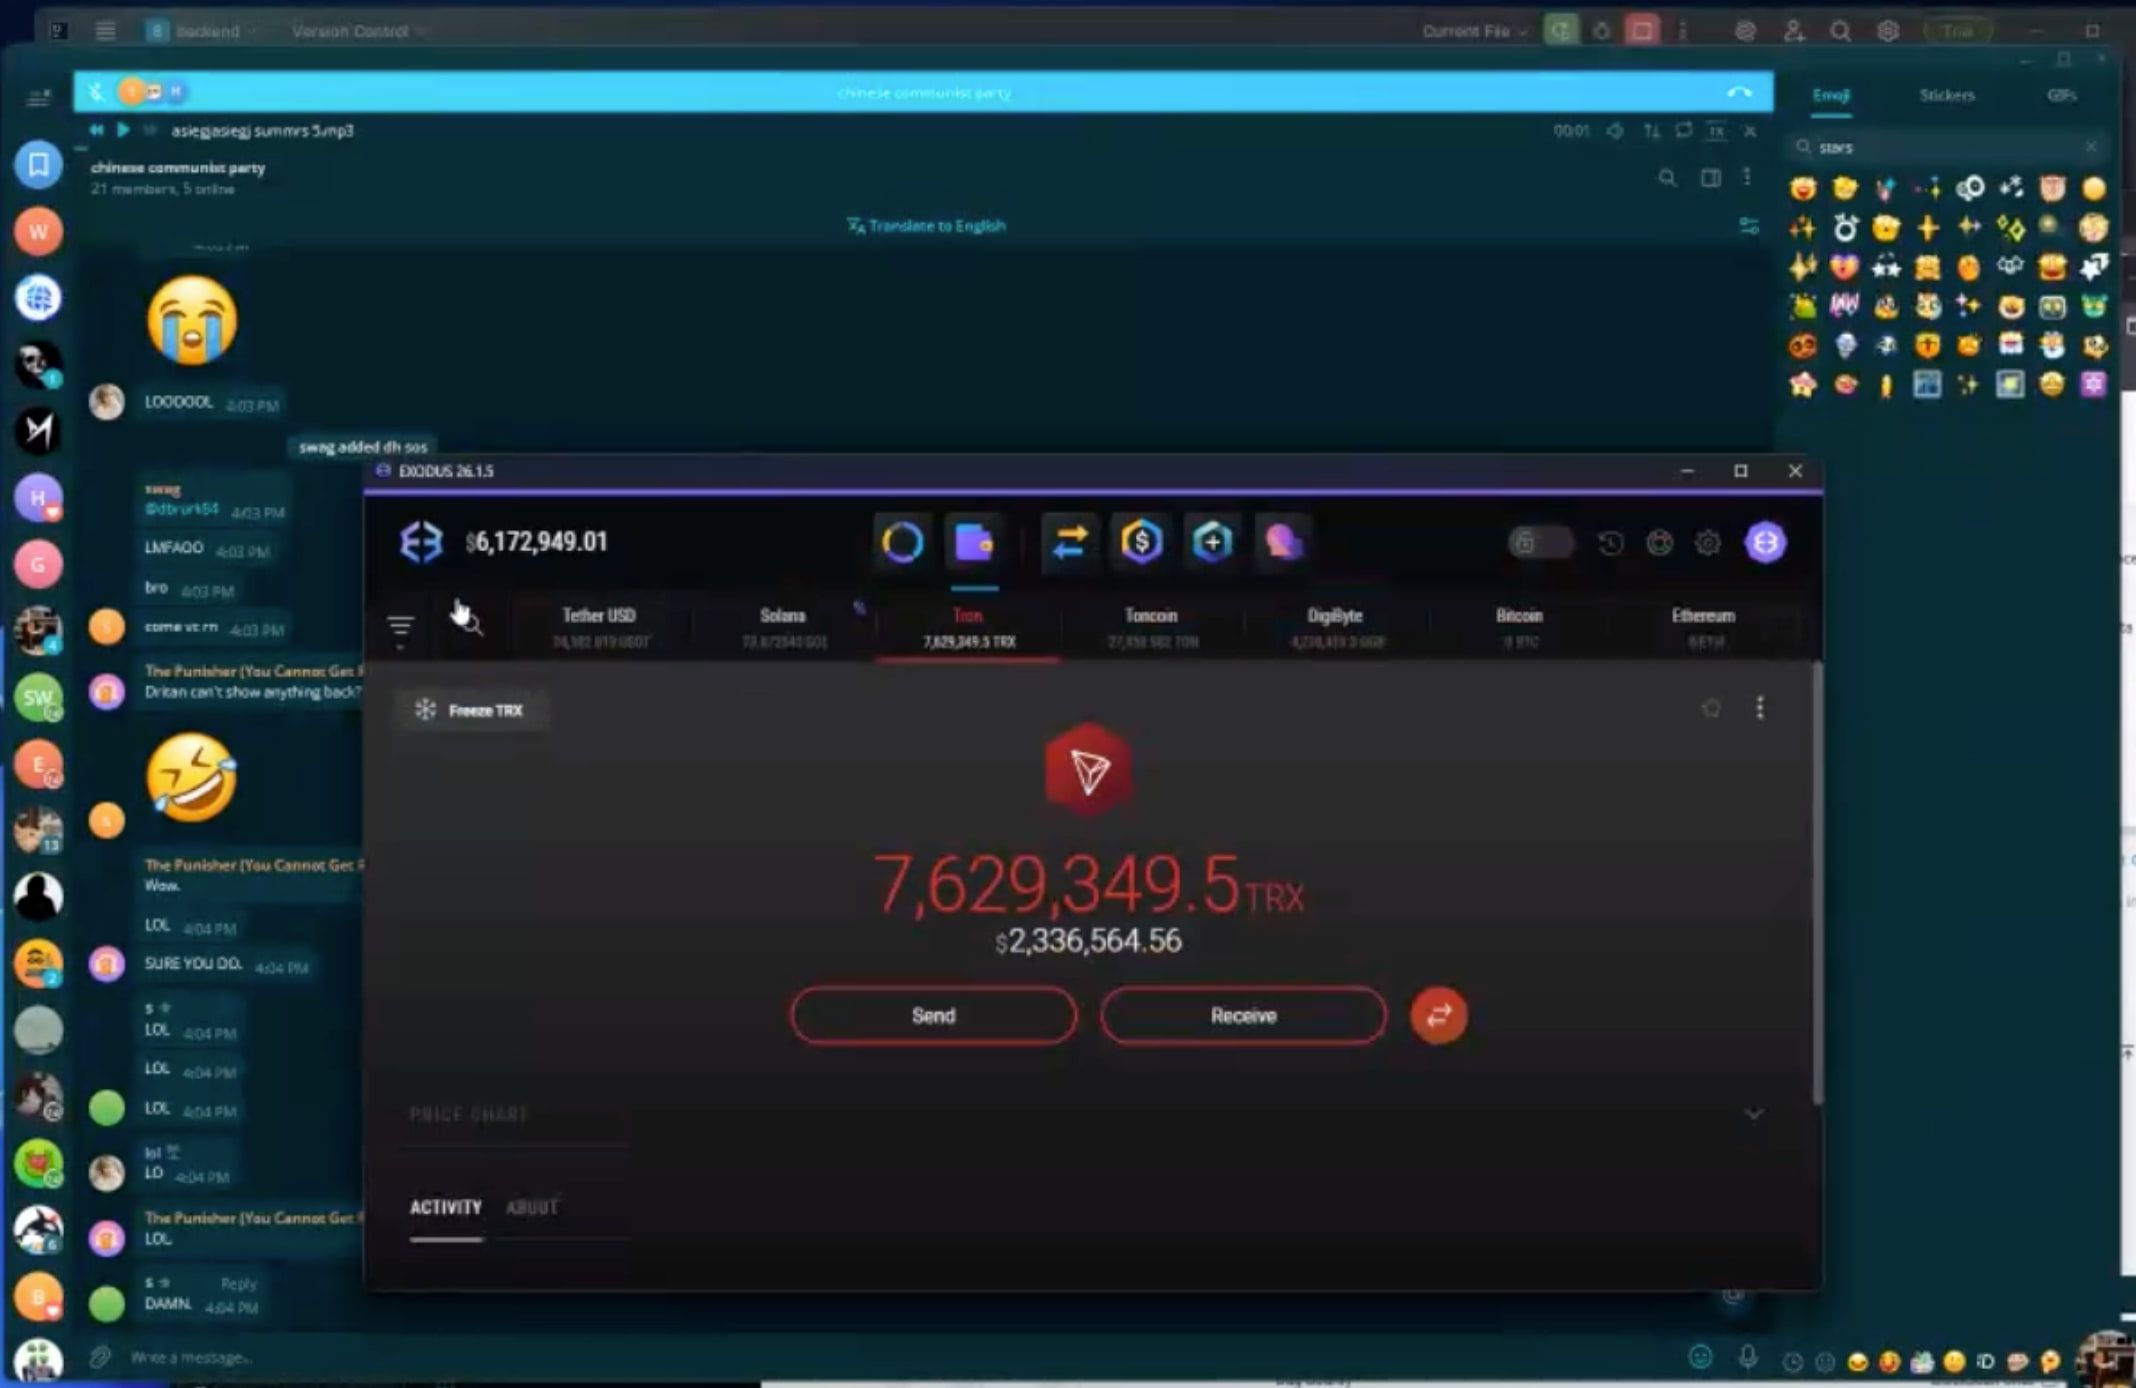
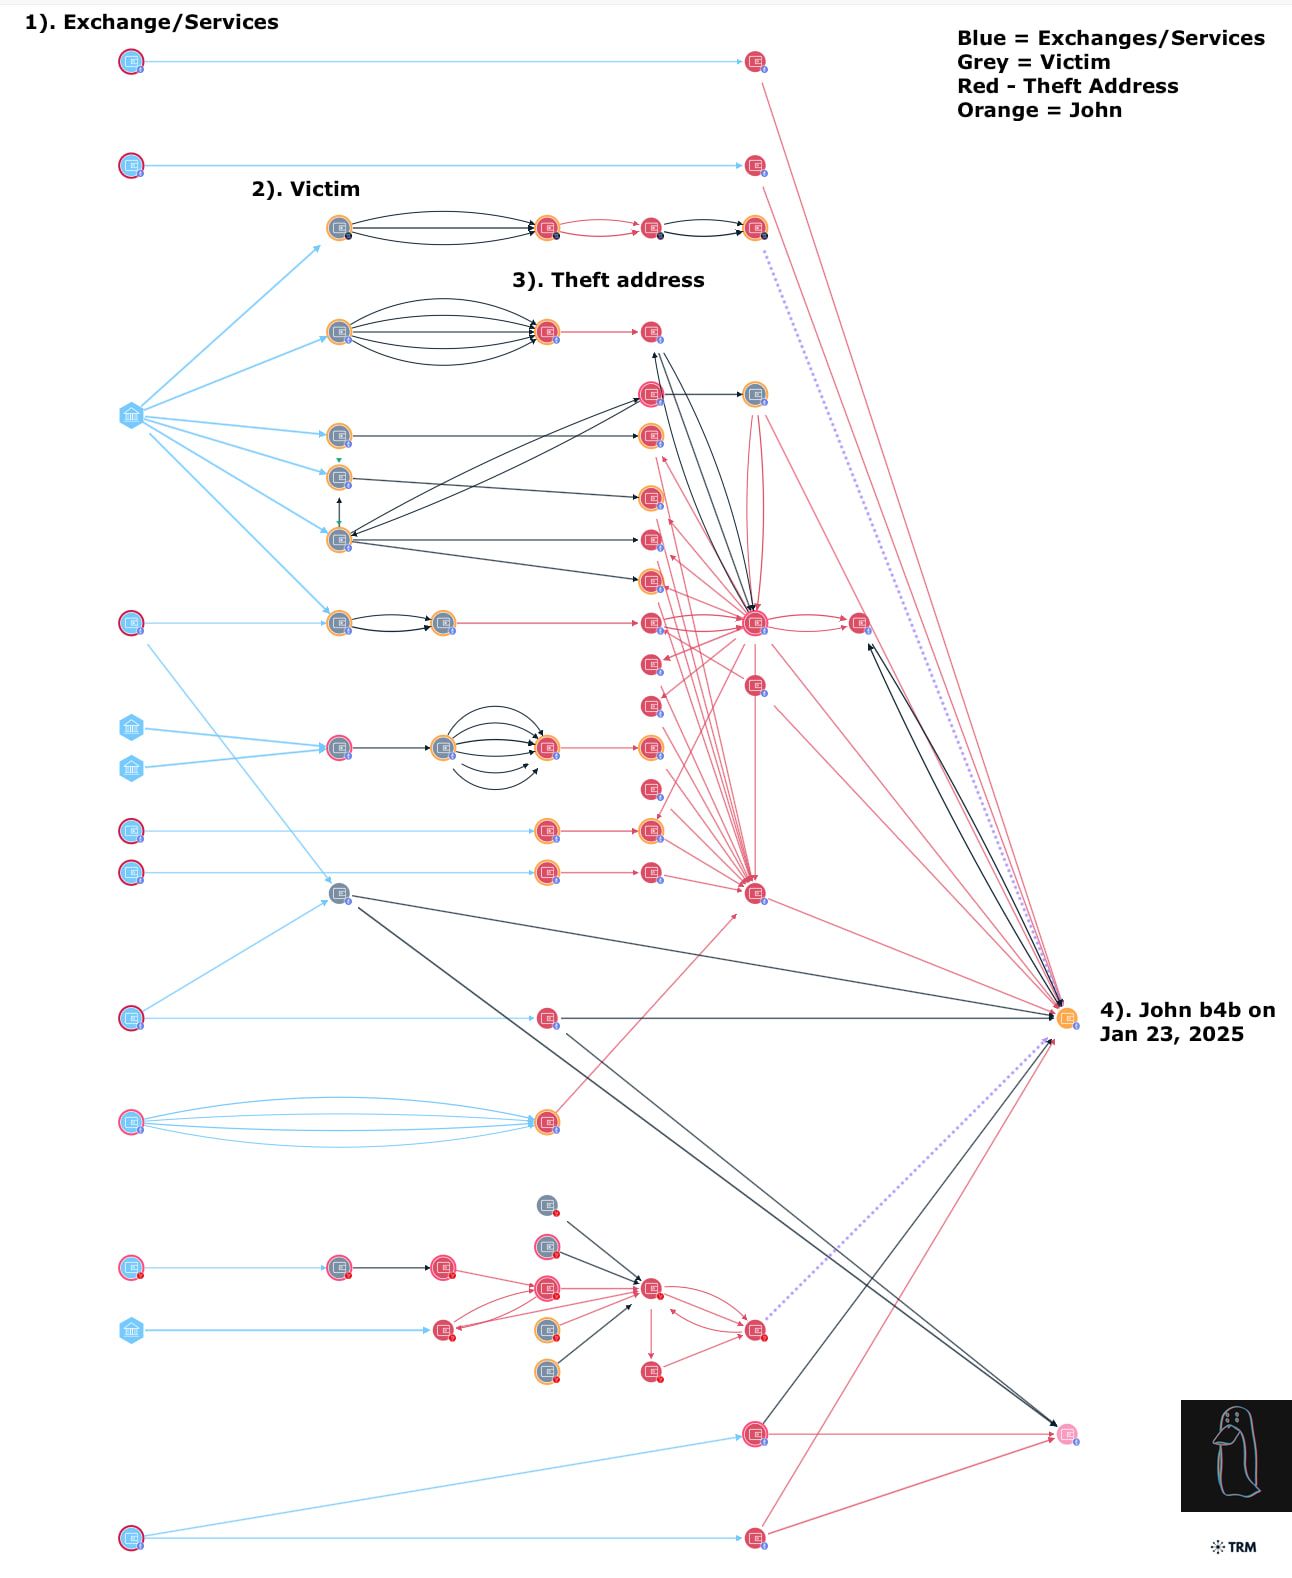
When $46 million in cryptocurrency held by the U.S. Government moved without explanation, the theft posed an unusual question: who steals from a government-held wallet? The investigation traced the stolen funds through peel chains and swap services, connecting the laundering pattern to an online persona, “Lick,” and then connecting that persona to a real identity, John Daghita.
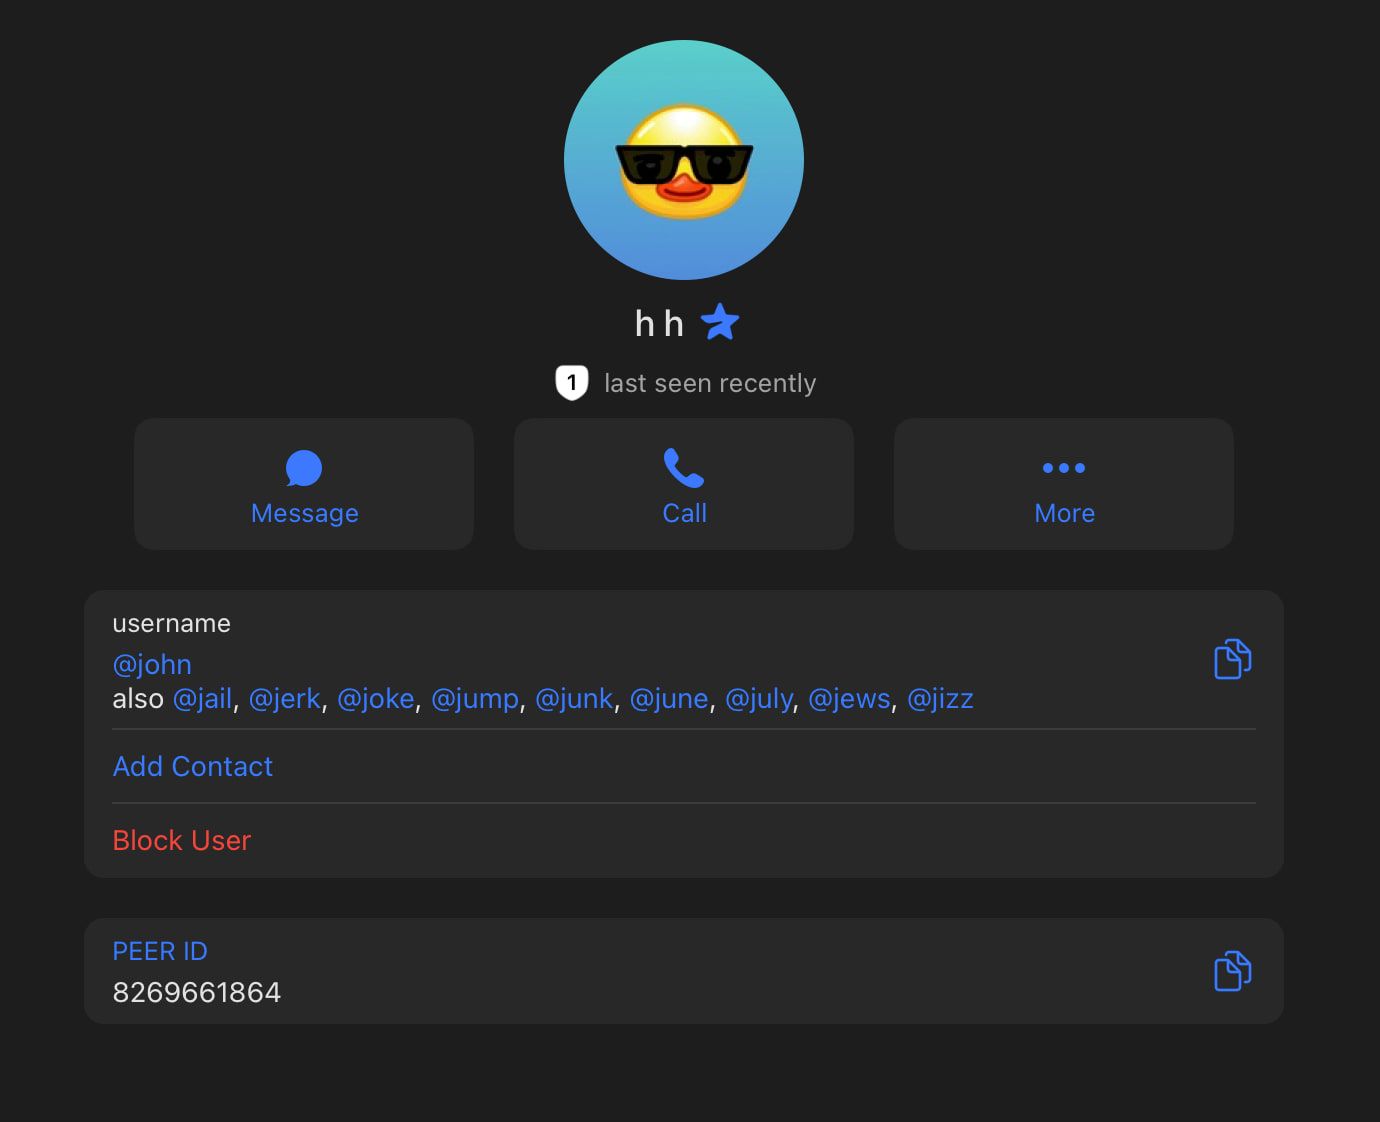
The attribution rested on the classic failure mode of crypto-native thieves: operational-security slips that link pseudonymous funding flows to accounts, usernames, and deposits tied to a real person. A second thread laid out the additional corroborating evidence.
Within weeks, an arrest in the case was publicly announced, along with a large recovery of funds (the amount is not public). The episode reinforced a pattern seen across these investigations: public attribution built on open blockchain data can move faster than the formal process.
Late 2025
$46M in U.S. Government-held cryptocurrency is moved by an unauthorized party and begins flowing through peel chains and swap services.
January 23, 2026
Investigation published attributing the theft to the persona “Lick,” identified as John Daghita; a follow-up thread adds corroborating evidence.
March 5, 2026+6 weeks
An arrest in the case is publicly announced, along with a large recovery of funds.