The Munchables protocol was exploited for $62M by an embedded DPRK IT worker; within a day, pressure and negotiation produced a full return of funds.
Munchables, a game protocol on the Blast network, was drained of $62 million, not by an external hacker but by one of its own developers. The 'developer' turned out to be a DPRK IT worker operating under a false identity, with privileged access baked into the contracts from the start.
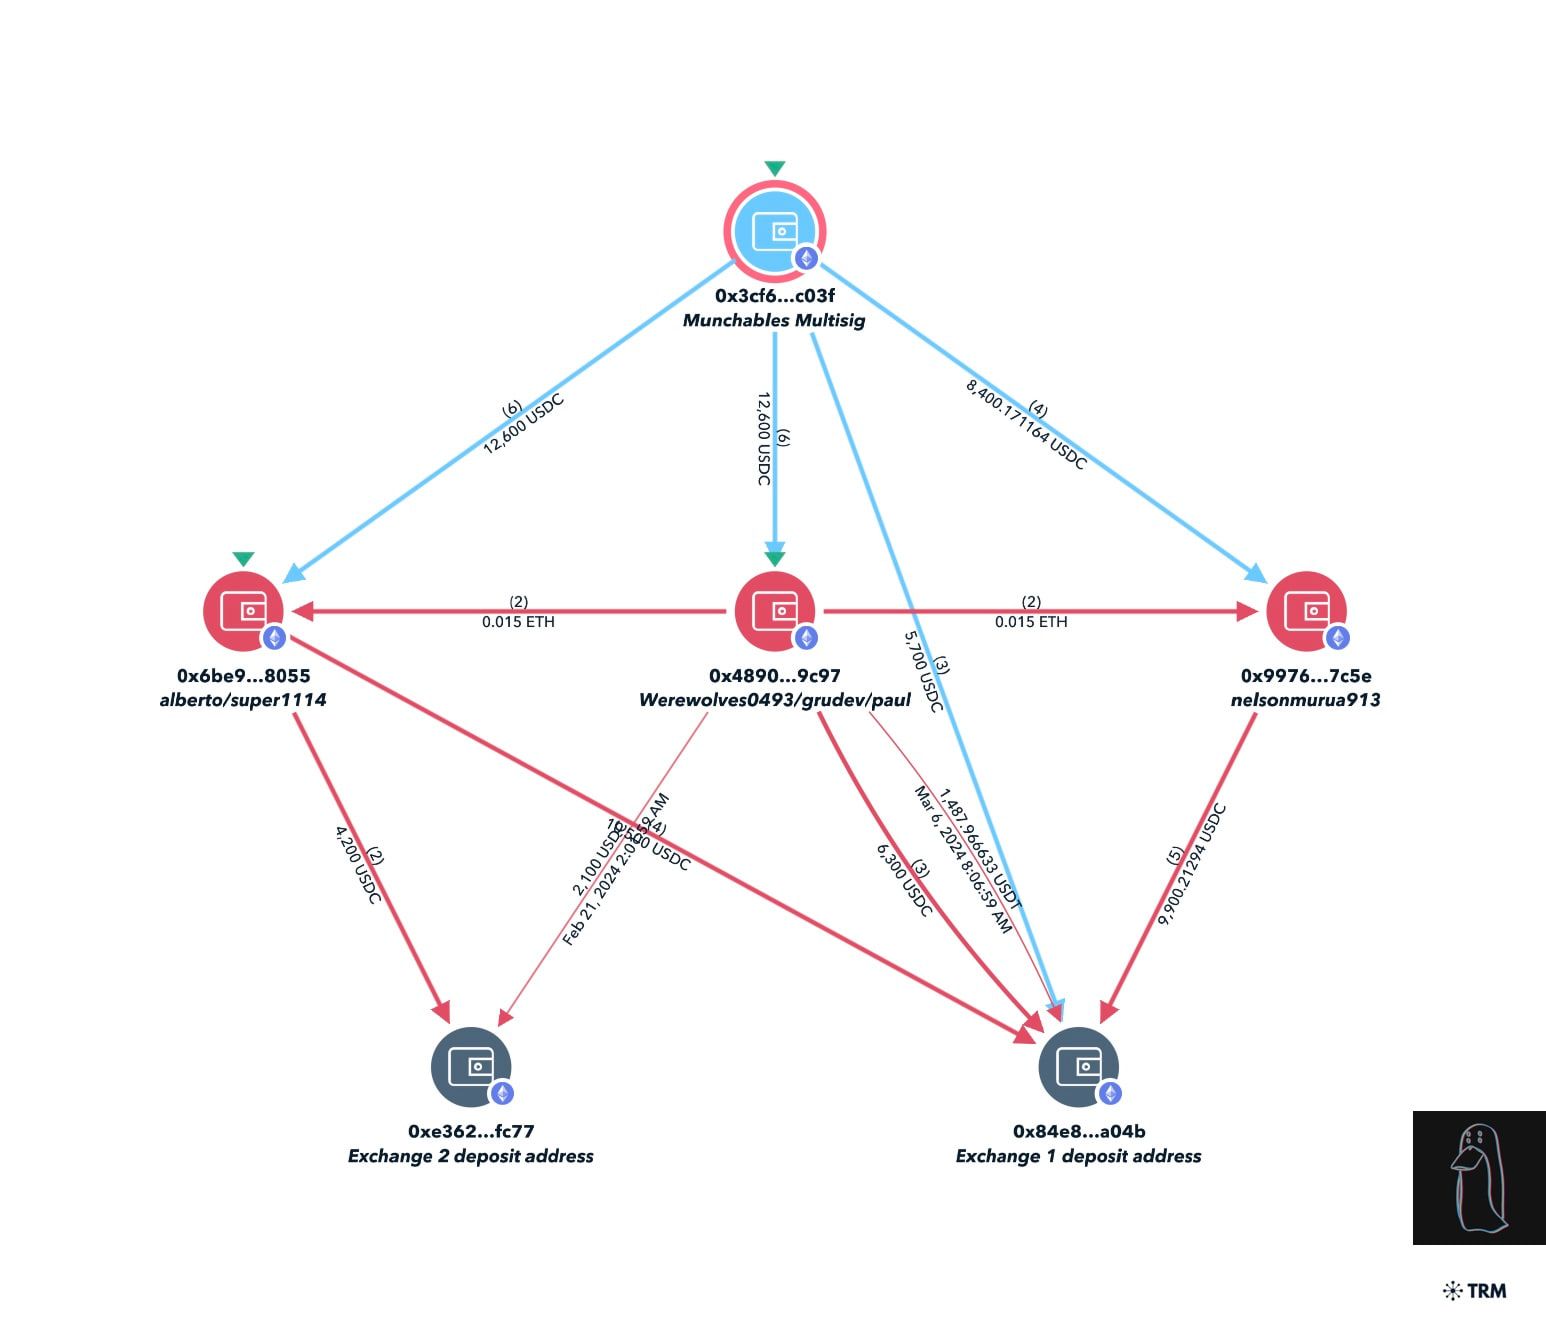
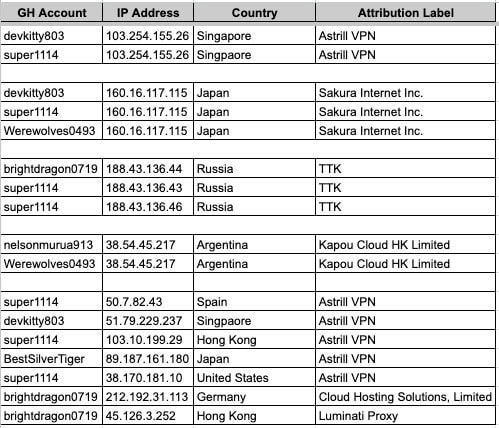
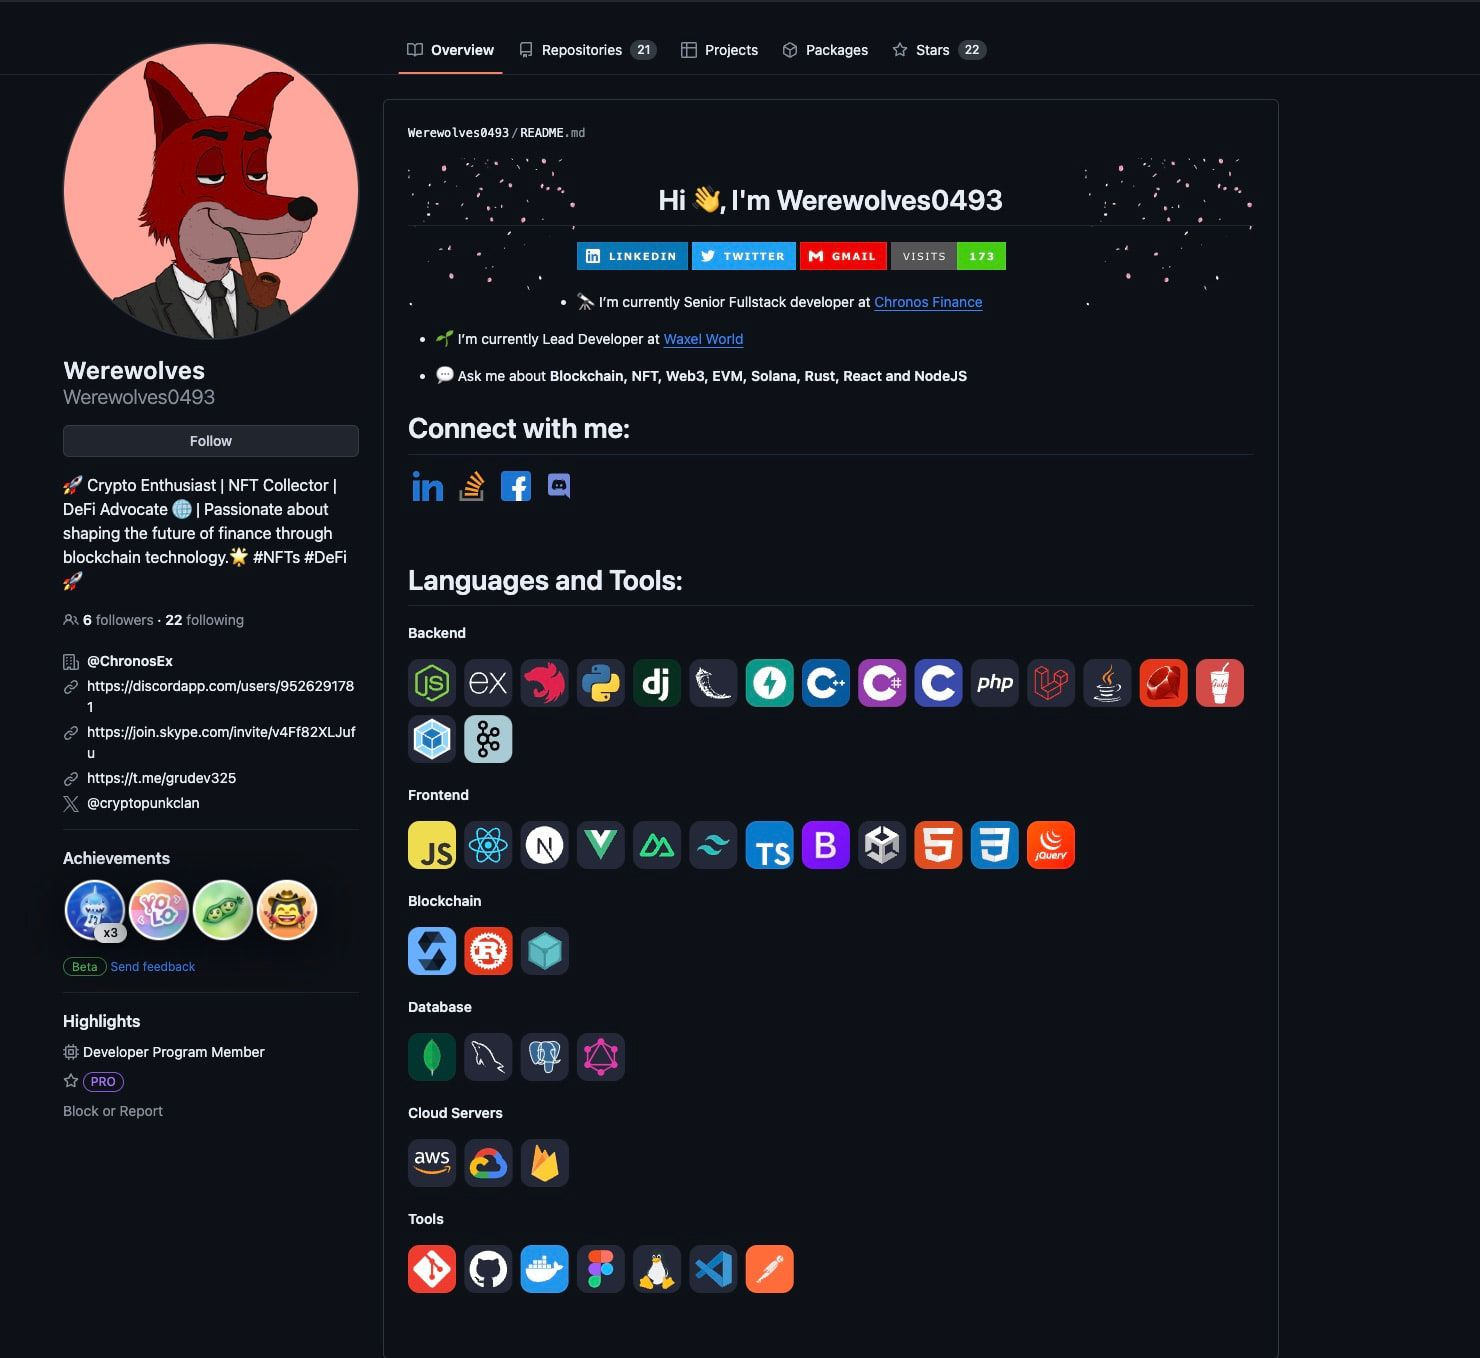
The attribution surfaced within hours: the developer identity was connected to a cluster of fake personas matching the known pattern of DPRK IT-worker infiltration, several of which appeared to be a single operator. With the exploiter publicly identified and boxed in ($62 million on a young network with thin exit liquidity is hard to launder), negotiation moved quickly.
Within roughly a day, the exploiter handed over the keys and the full $62 million was returned. It remains one of the largest full recoveries in DeFi history, and the clearest demonstration that speed of attribution can change an exploit's outcome entirely.
March 26, 2024
Munchables is exploited for $62M via privileged access held by an embedded developer.
March 26, 2024same day
The developer is publicly connected to a cluster of fake identities matching DPRK IT-worker infiltration patterns.
March 27, 2024+1 day
The exploiter relinquishes the keys; all $62M is recovered without any payment.