Investigation connecting 25+ exploits totaling over $200M to the Lazarus Group through shared laundering infrastructure; $7M recovered.
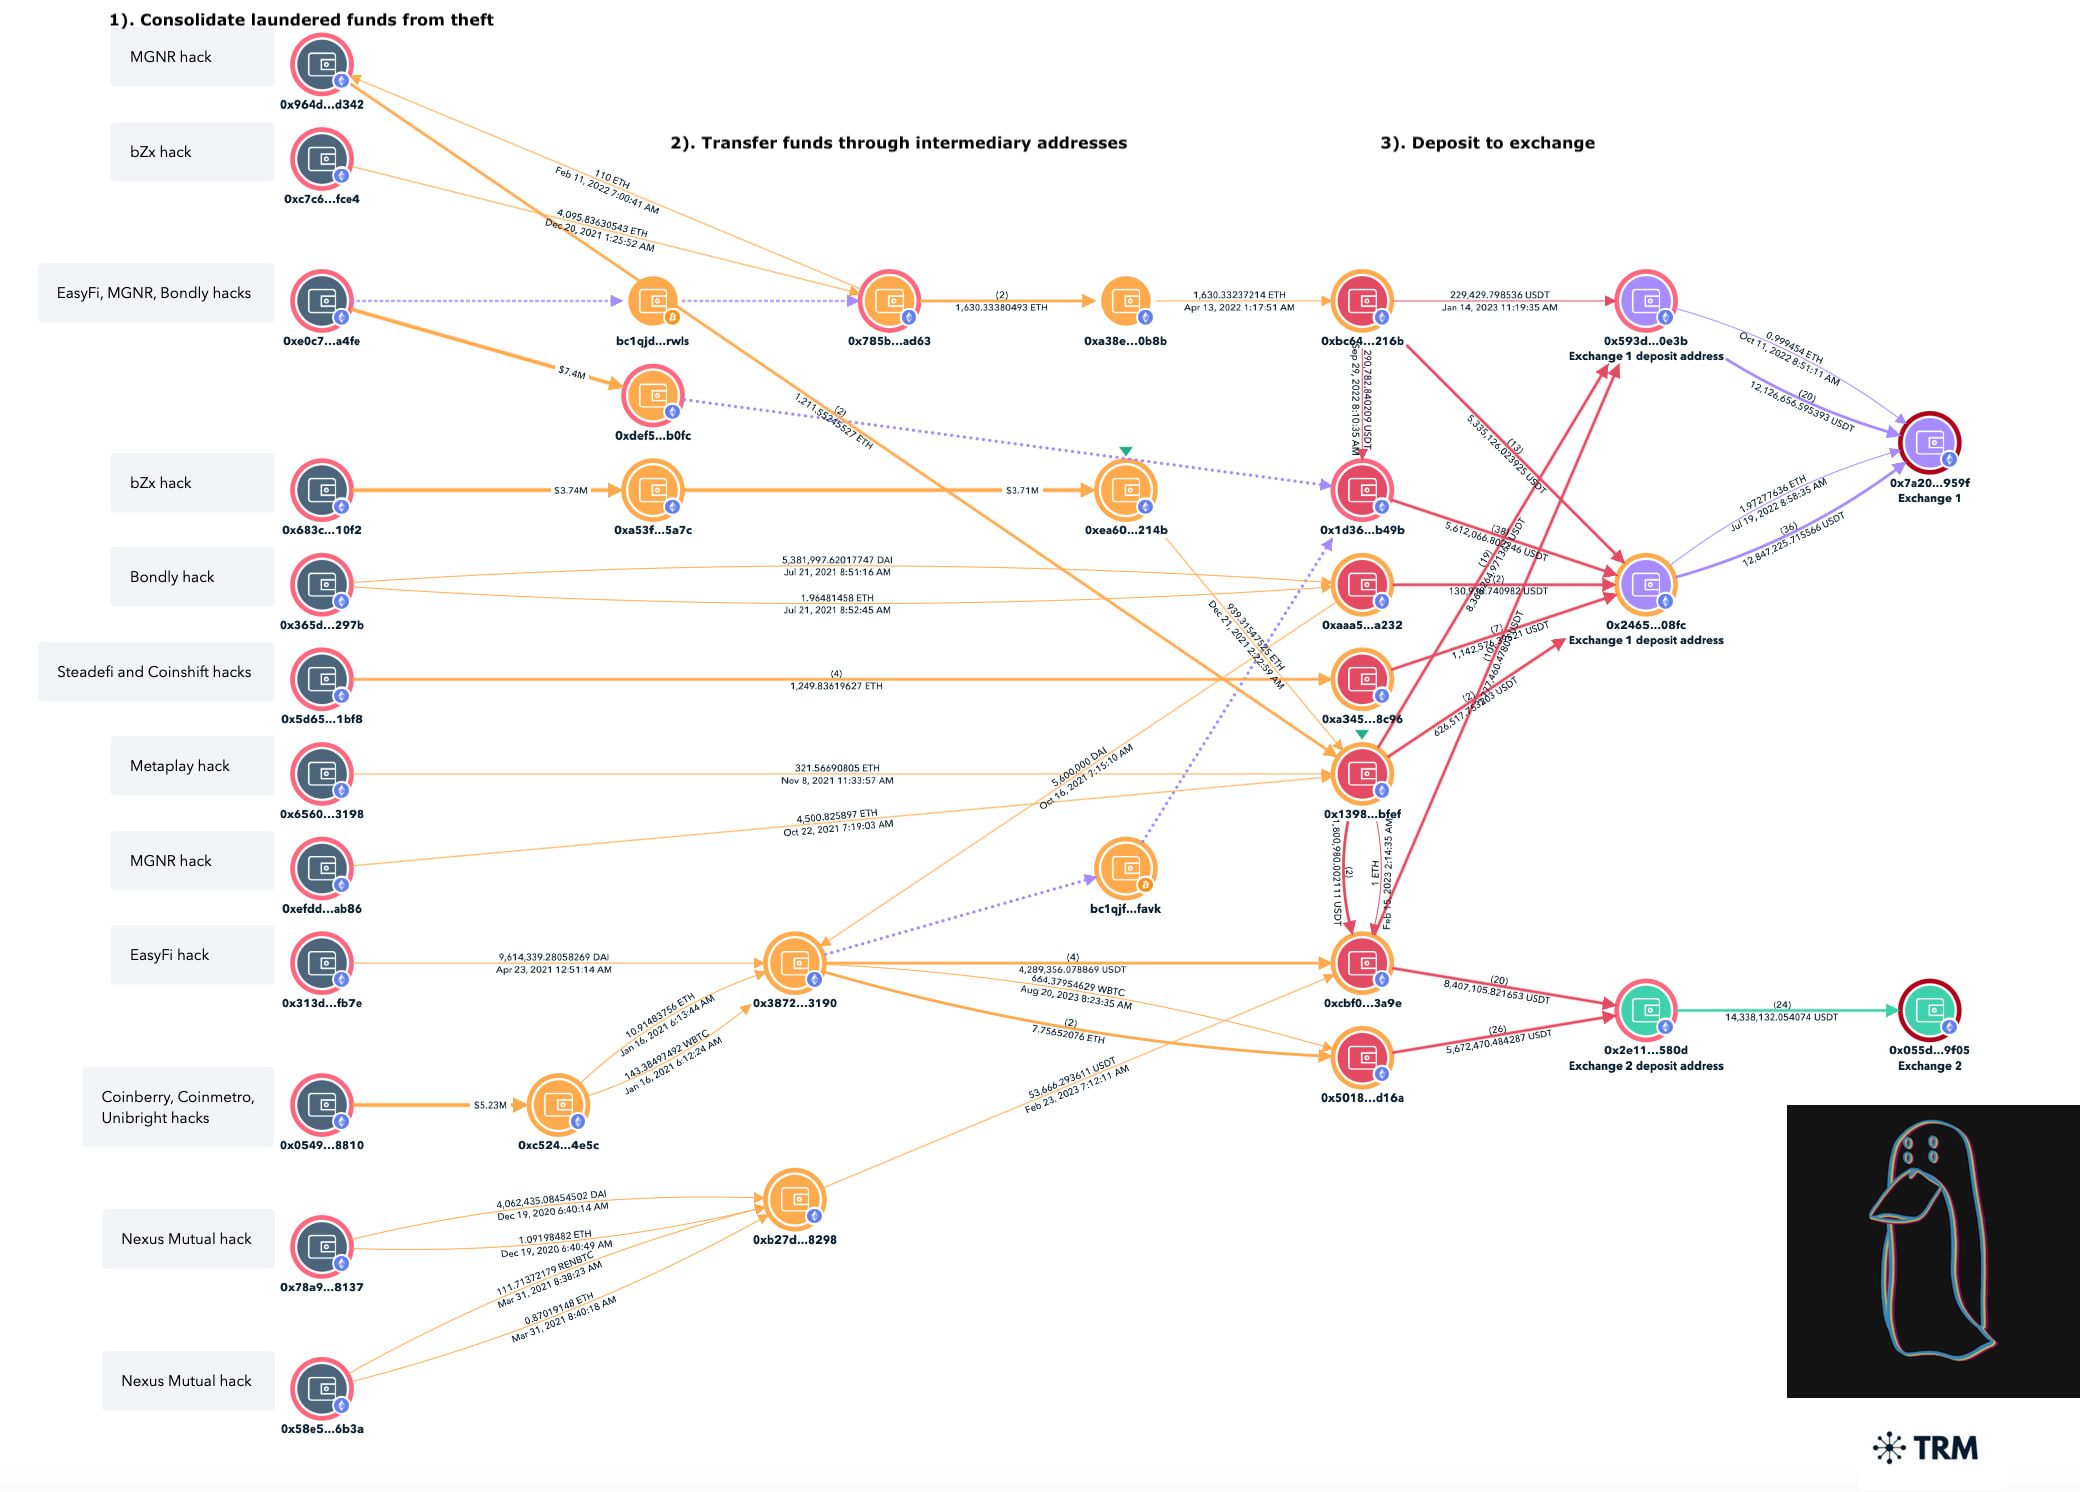
Individually, the hacks looked unrelated: two dozen protocols and platforms across chains and years. Followed to their cash-out points, they converged: the same laundering paths, the same P2P marketplaces, the same over-the-counter traders converting stolen crypto to fiat.
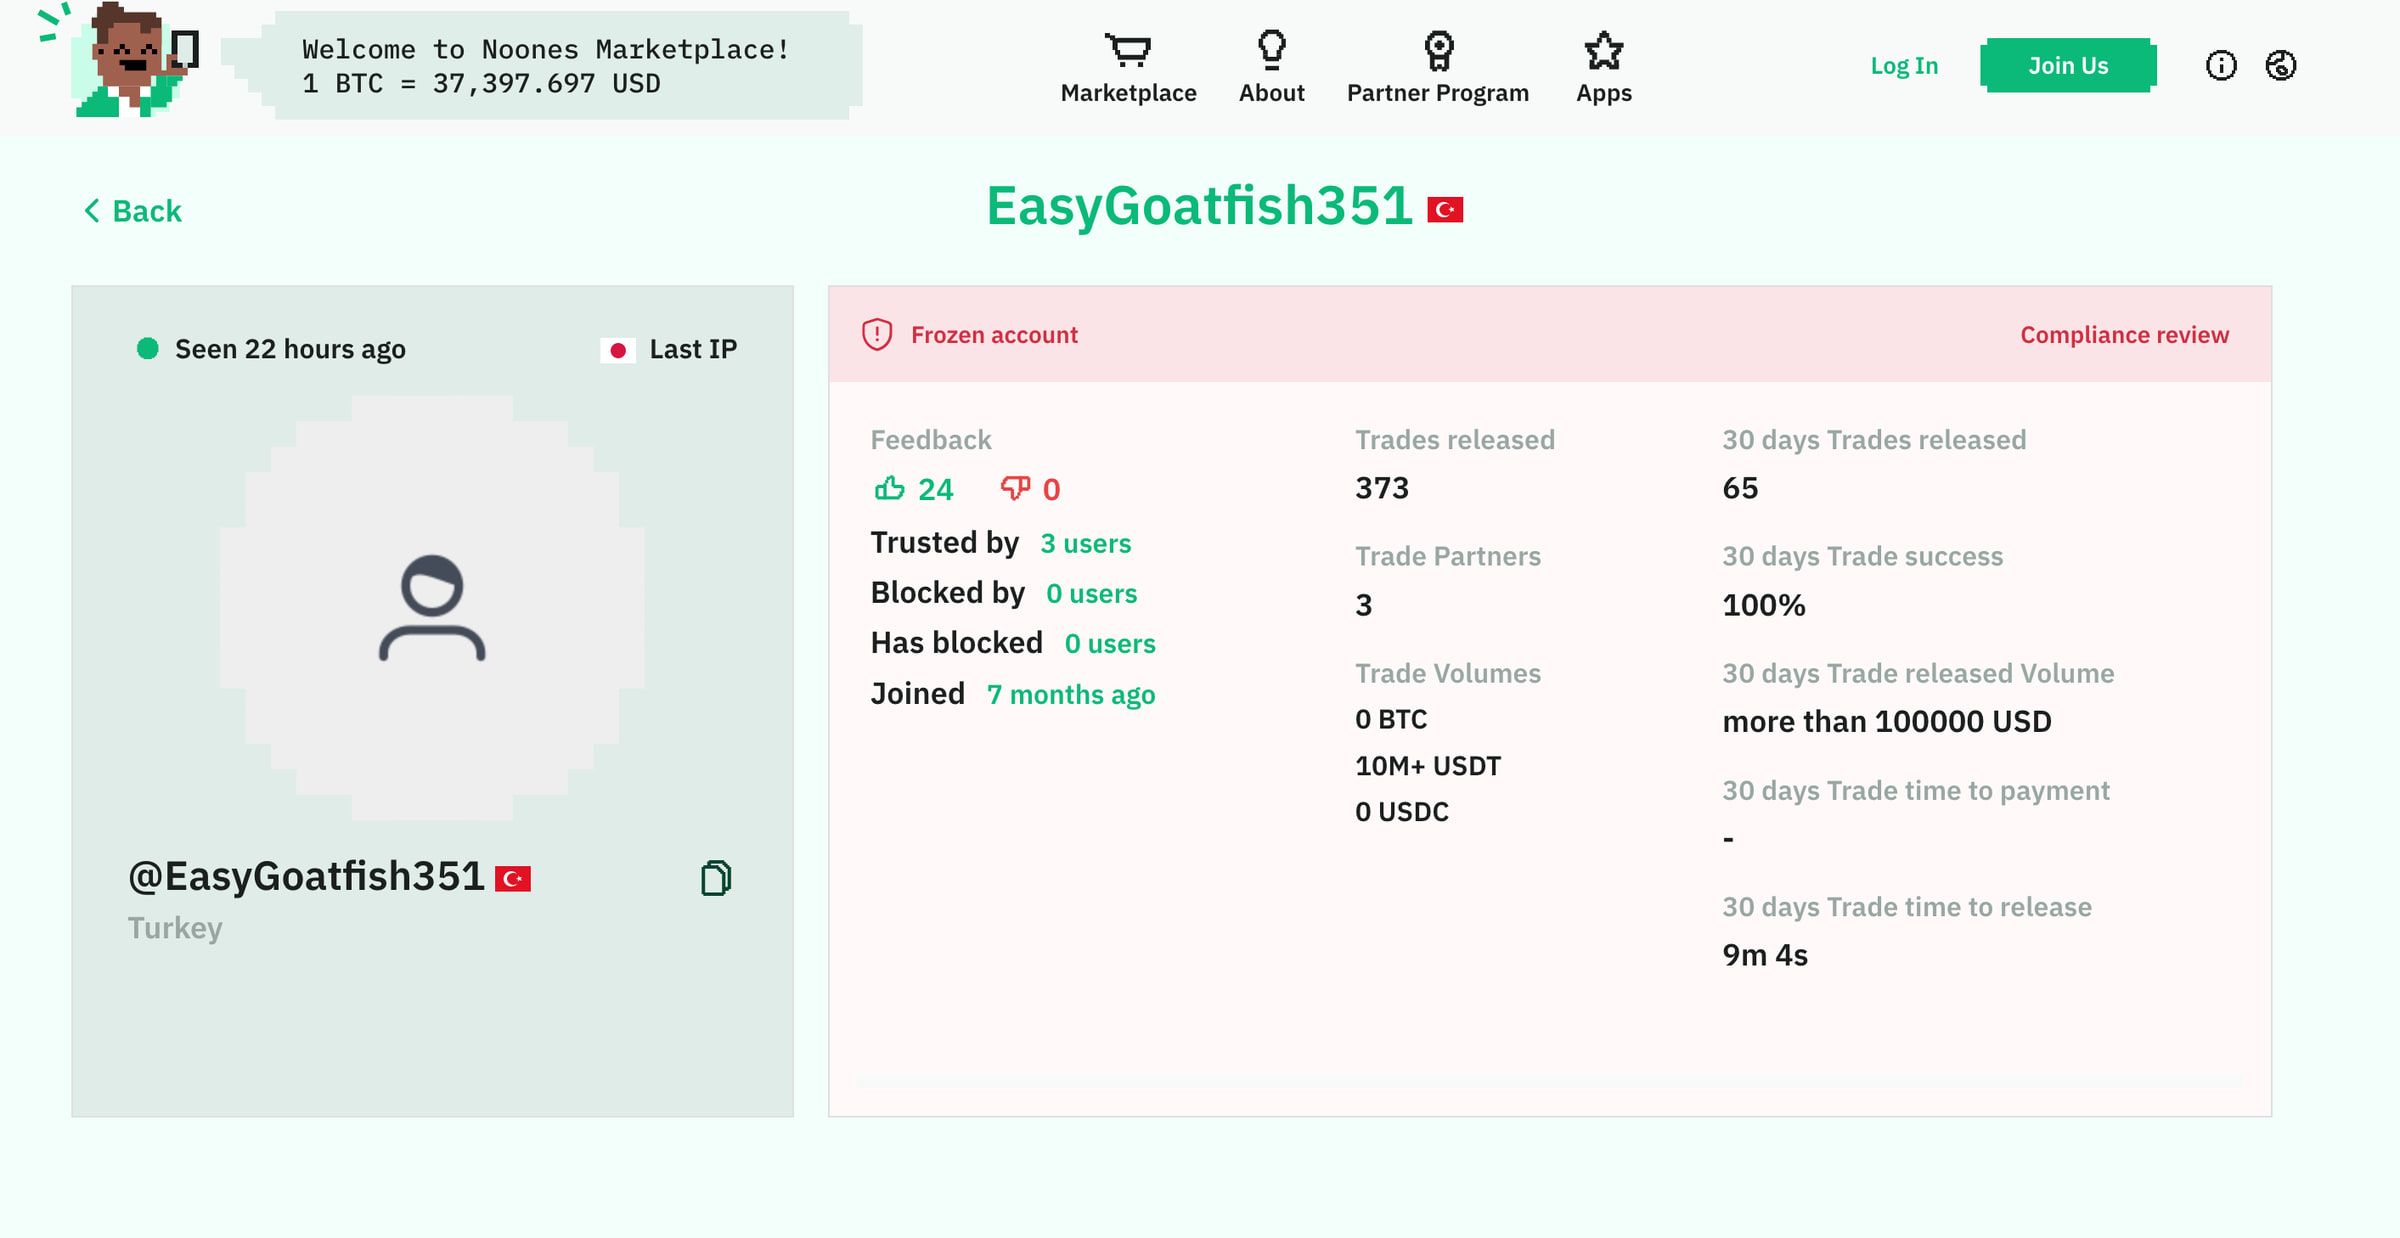
The investigation tied more than 25 exploits, totaling over $200 million, to the Lazarus Group, North Korea's state hacking apparatus. The connective tissue was the laundering layer: however varied the intrusions, the money kept flowing through common infrastructure, including identifiable OTC networks used to convert USDT to cash.
Beyond attribution, the work had teeth: roughly $7 million was recovered through the tracing, and stablecoin issuers blacklisted addresses in the cash-out network. The investigation stands as one of the most complete public maps of how DPRK-stolen funds actually reach fiat.
2020–2023
A long series of seemingly unrelated protocol hacks accumulates across chains, later shown to share a cash-out layer.
April 29, 2024
Investigation published connecting 25+ exploits totaling $200M+ to the Lazarus Group via common laundering and OTC infrastructure.
April 2024
$7M recovered; stablecoin issuers blacklist addresses in the identified cash-out network.
Investigation: connecting 25+ exploits and $200M+ in stolen funds to the Lazarus Group through their shared laundering and cash-out network.
 ZachXBT@zachxbtApril 2024
Long-form write-up: how the Lazarus Group laundered $200M from 25+ hacks to fiat between 2020 and 2023, with the full address list.
ZachXBT@zachxbtApril 2024