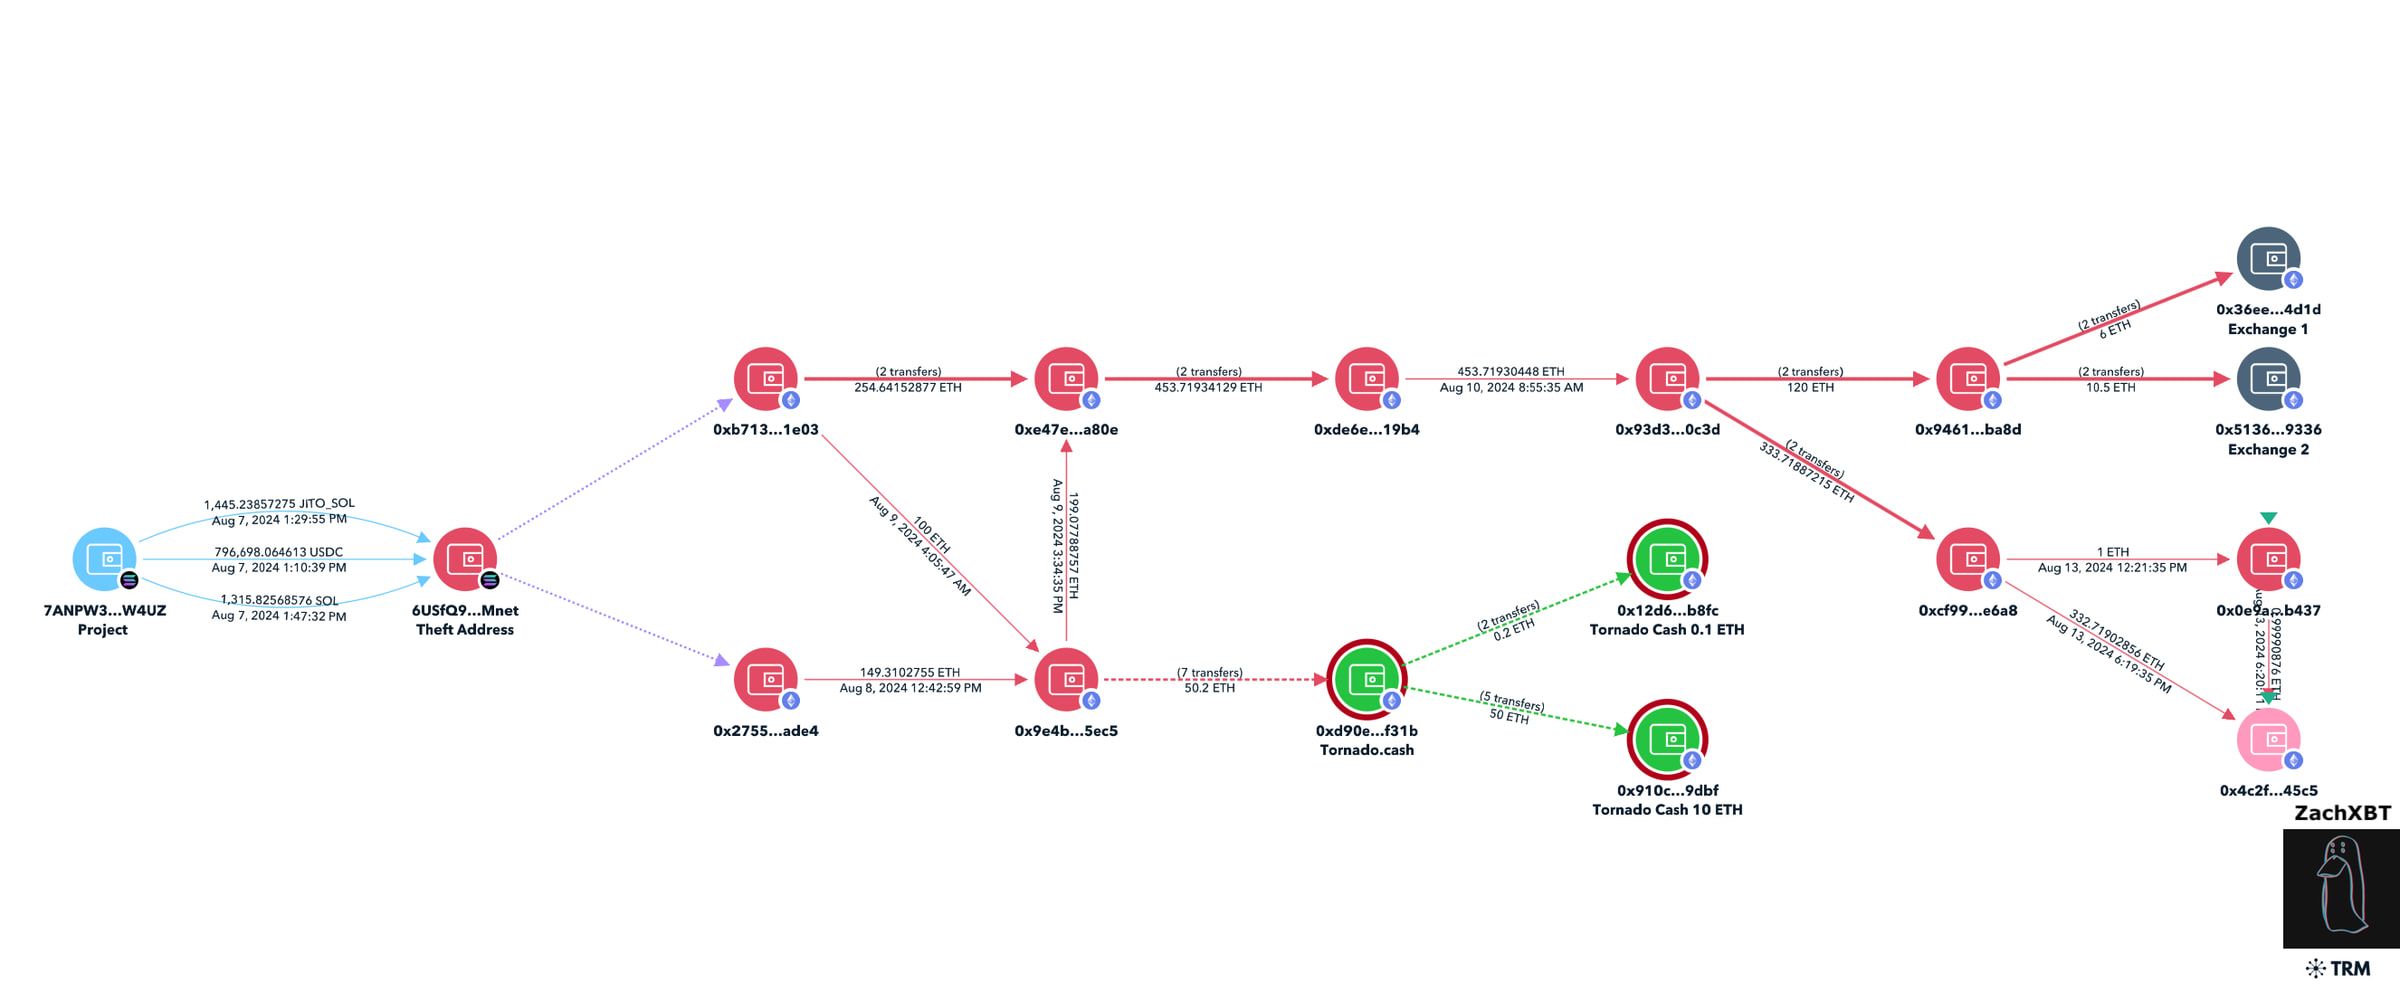
A project unknowingly hired DPRK IT workers who exploited it for $1.3M; rapid tracing recovered $1M and exposed the hiring network behind it.
A crypto project discovered the hard way that several of its 'remote developers' were DPRK IT workers operating under false identities. Once embedded, the operators exploited their access to drain roughly $1.3 million from the project's treasury.
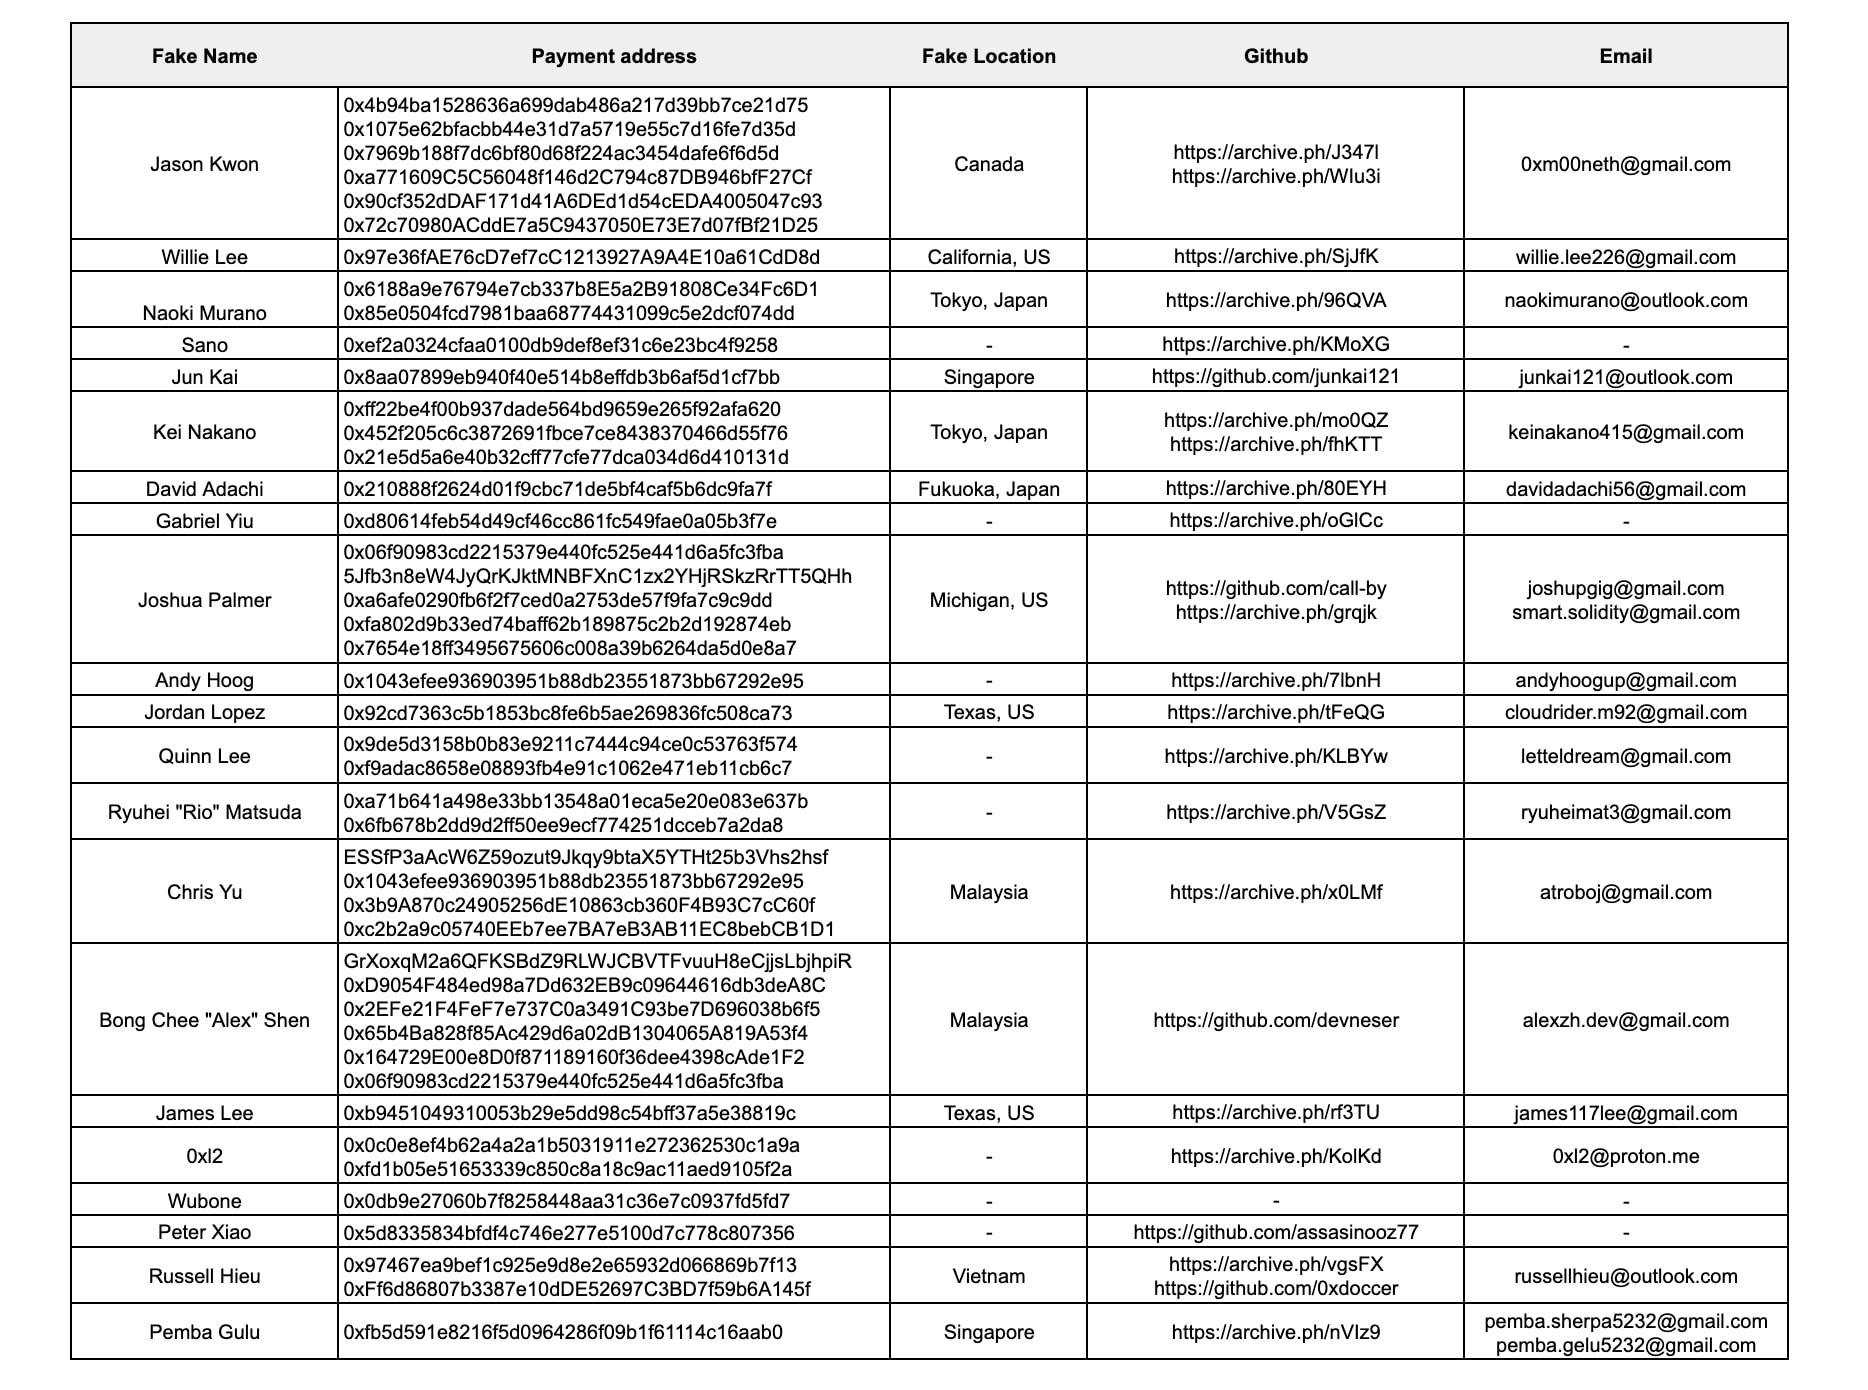
Because the theft was detected and traced quickly, most of the funds never escaped: $1 million was recovered. The investigation went further than the single incident, documenting how the same cluster of fake developer identities had cycled through multiple projects: shared payment addresses, recycled résumés, and overlapping GitHub activity connecting supposedly independent contractors.
The thread became a widely-cited reference for teams screening remote hires, and part of the broader body of work mapping how DPRK IT workers infiltrate the industry.
August 2024
A project's treasury is exploited for $1.3M; the attackers are identified as DPRK IT workers hired under false identities.
August 15, 2024
Rapid tracing enables recovery of $1M. Investigation published mapping the fake-developer network across multiple victim projects.